SlingStrike ships realistic attack log sequences directly to your SIEM - so you know your rules work before attackers test them.
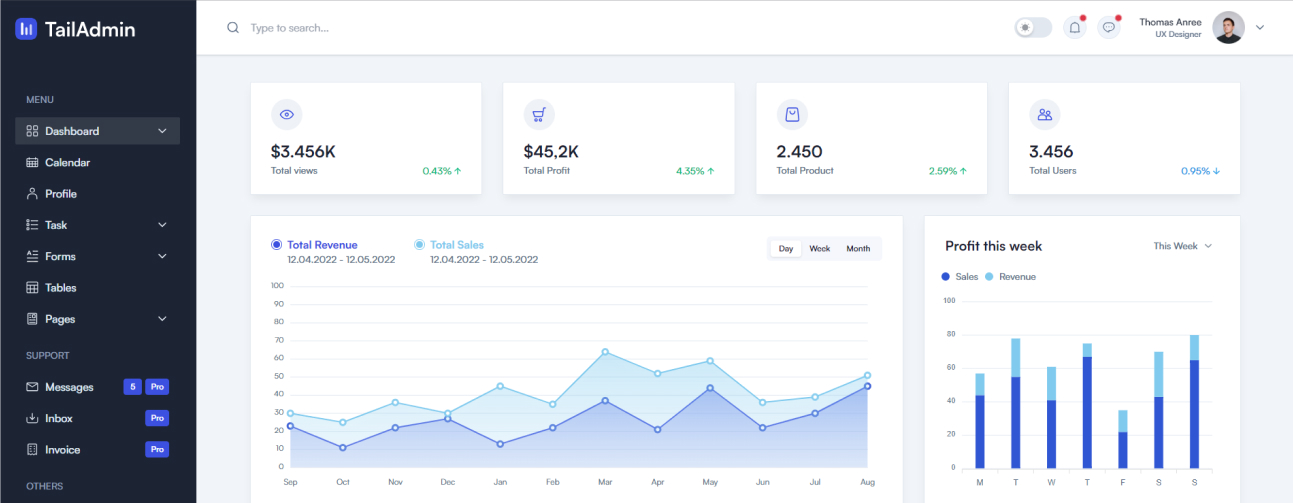
Discover the core capabilities that make SlingStrike a powerful, flexible and efficient platform for building and testing SIEM use cases.
SlingStrike is fully open‑source, giving security teams complete transparency, flexibility and control. You can inspect the code, customize the framework and contribute improvements - without licensing fees or vendor lock‑in.
Learn MoreDesigned for versatility, SlingStrike supports building, testing and validating SIEM correlation rules and use cases across different platforms. Whether you’re developing new detections or refining existing ones, the framework adapts to your workflow.
Learn MoreThe architecture is clean, modular, and built for reliability. Every component is crafted to simplify complex tasks, reduce friction and help analysts focus on detection engineering instead of tooling issues.
Learn MoreSlingStrike comes with all the core capabilities needed for effective rule development-log parsing, event simulation, testing utilities and REST API calls - so you can start creating and validating detections immediately.
Learn More
SlingStrike gives SOC or CyberSec engineers a powerful, streamlined toolkit for creating and validating SIEM use cases with speed and confidence. From simulating events to verifying correlation logic, every tool is built to cut development time and eliminate guesswork.
You get a smooth, repeatable workflow that helps you ship stronger detections in a fraction of the time.
Unlock the full power of SlingStrike and jumpstart your journey to building smarter, faster and more effective SIEM use cases today.
Start using SlingStrikeNo subscriptions. The community edition is free forever - enterprise packs and features are a one-time purchase, per instance.
Full application, self-hosted
All community use cases (GitHub)
Unlimited SIEM targets, all log formats
Docker Compose deployment
Bare metal deployment
Community support (GitHub Issues)
Recommended
Enterprise - Perpetual LicenseCurated
MITRE ATT&CK-mapped Use cases
Multi-user RBAC model, Audit log
Audit log
LDAP / Active Directory integration
Perpetual - no expiry
All minor & major app updates during the term
Updates to already-purchased content packs
Security patches
Expires gracefully - your instance keeps working
Find clear, concise answers to the most important questions about SlingStrike and its capabilities.
SlingStrike streamlines the entire process of building, testing and validating SIEM use cases, helping you work faster, reduce manual effort, and deliver higher‑quality detections with confidence.
Yes - the framework is designed to be flexible and platform‑agnostic, allowing you to integrate it into most SIEM environments and adapt it to your current data pipelines and workflows.
It provides a dedicated environment with predefined patterns and functions for simulation, correlation testing, rule validation and iterative development - capabilities that traditional SIEMs often lack or make difficult to perform efficiently.
SlingStrike is built with simplicity and clarity in mind, supported by documentation and an open‑source community. You can get started quickly and maintain it with minimal overhead.
Our focus is practical tooling that helps engineers and analysts simulate attack logs, validate correlation rules and build confidence in their detections.
401 Broadway, 24th Floor, Orchard Cloud View, London
slingstrike@proton.me